Lorne & Vale Get started

Security

Secure today
Secure after quantum

Your documents are sealed with the post-quantum encryption standardised by NIST, your record’s checkpoints carry post-quantum signatures, and connections use a post-quantum key exchange on devices that support it. All of it is hosted in Europe and walled off for your company alone. Here is how it works, in plain words, with demonstrations you can try yourself.

  • Post-quantum encryption
  • Hosted in Europe
  • Chained record, signed checkpoints
  • Access for your team only

Live demonstration

What you see
What an intruder sees

Every document is encrypted before it is stored. Switch the view: your browser encrypts this text right now, with the algorithm that seals your documents.

Quote_Rossi_Plomberie.pdf

Rossi Plomberie

Room 4: replace the thermostatic valve and bleed the circuit.

€640 excl. VAT. Work possible on Thursday at 9:00.

The same quote, as it is stored: a string of characters that means nothing without the key.

Algorithm
AES-256-GCM
Key
256 bits, new for this document
Key locked by
X25519 + ML-KEM-1024
Stored in
Europe

A new key and a different result every time. Without the key, there is nothing to read.

Post-quantum, explained

Copied today
Still sealed tomorrow

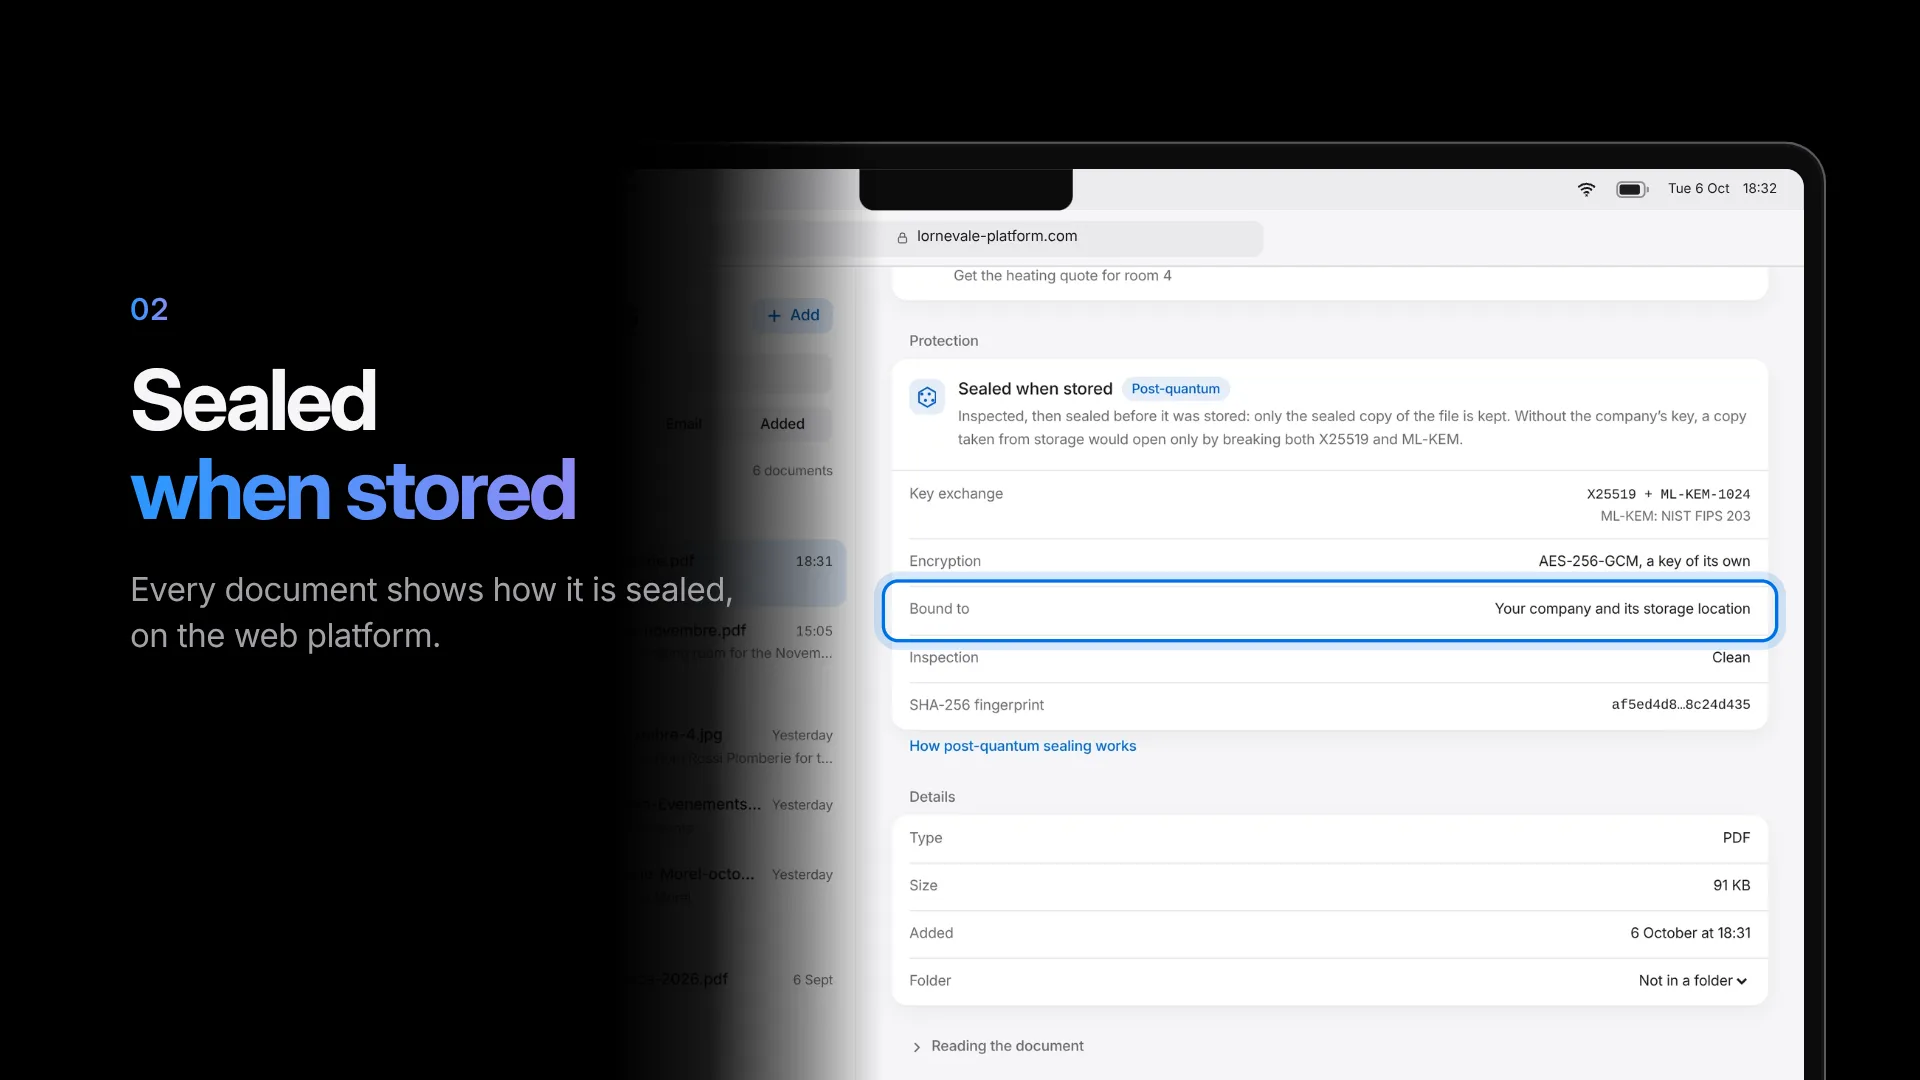
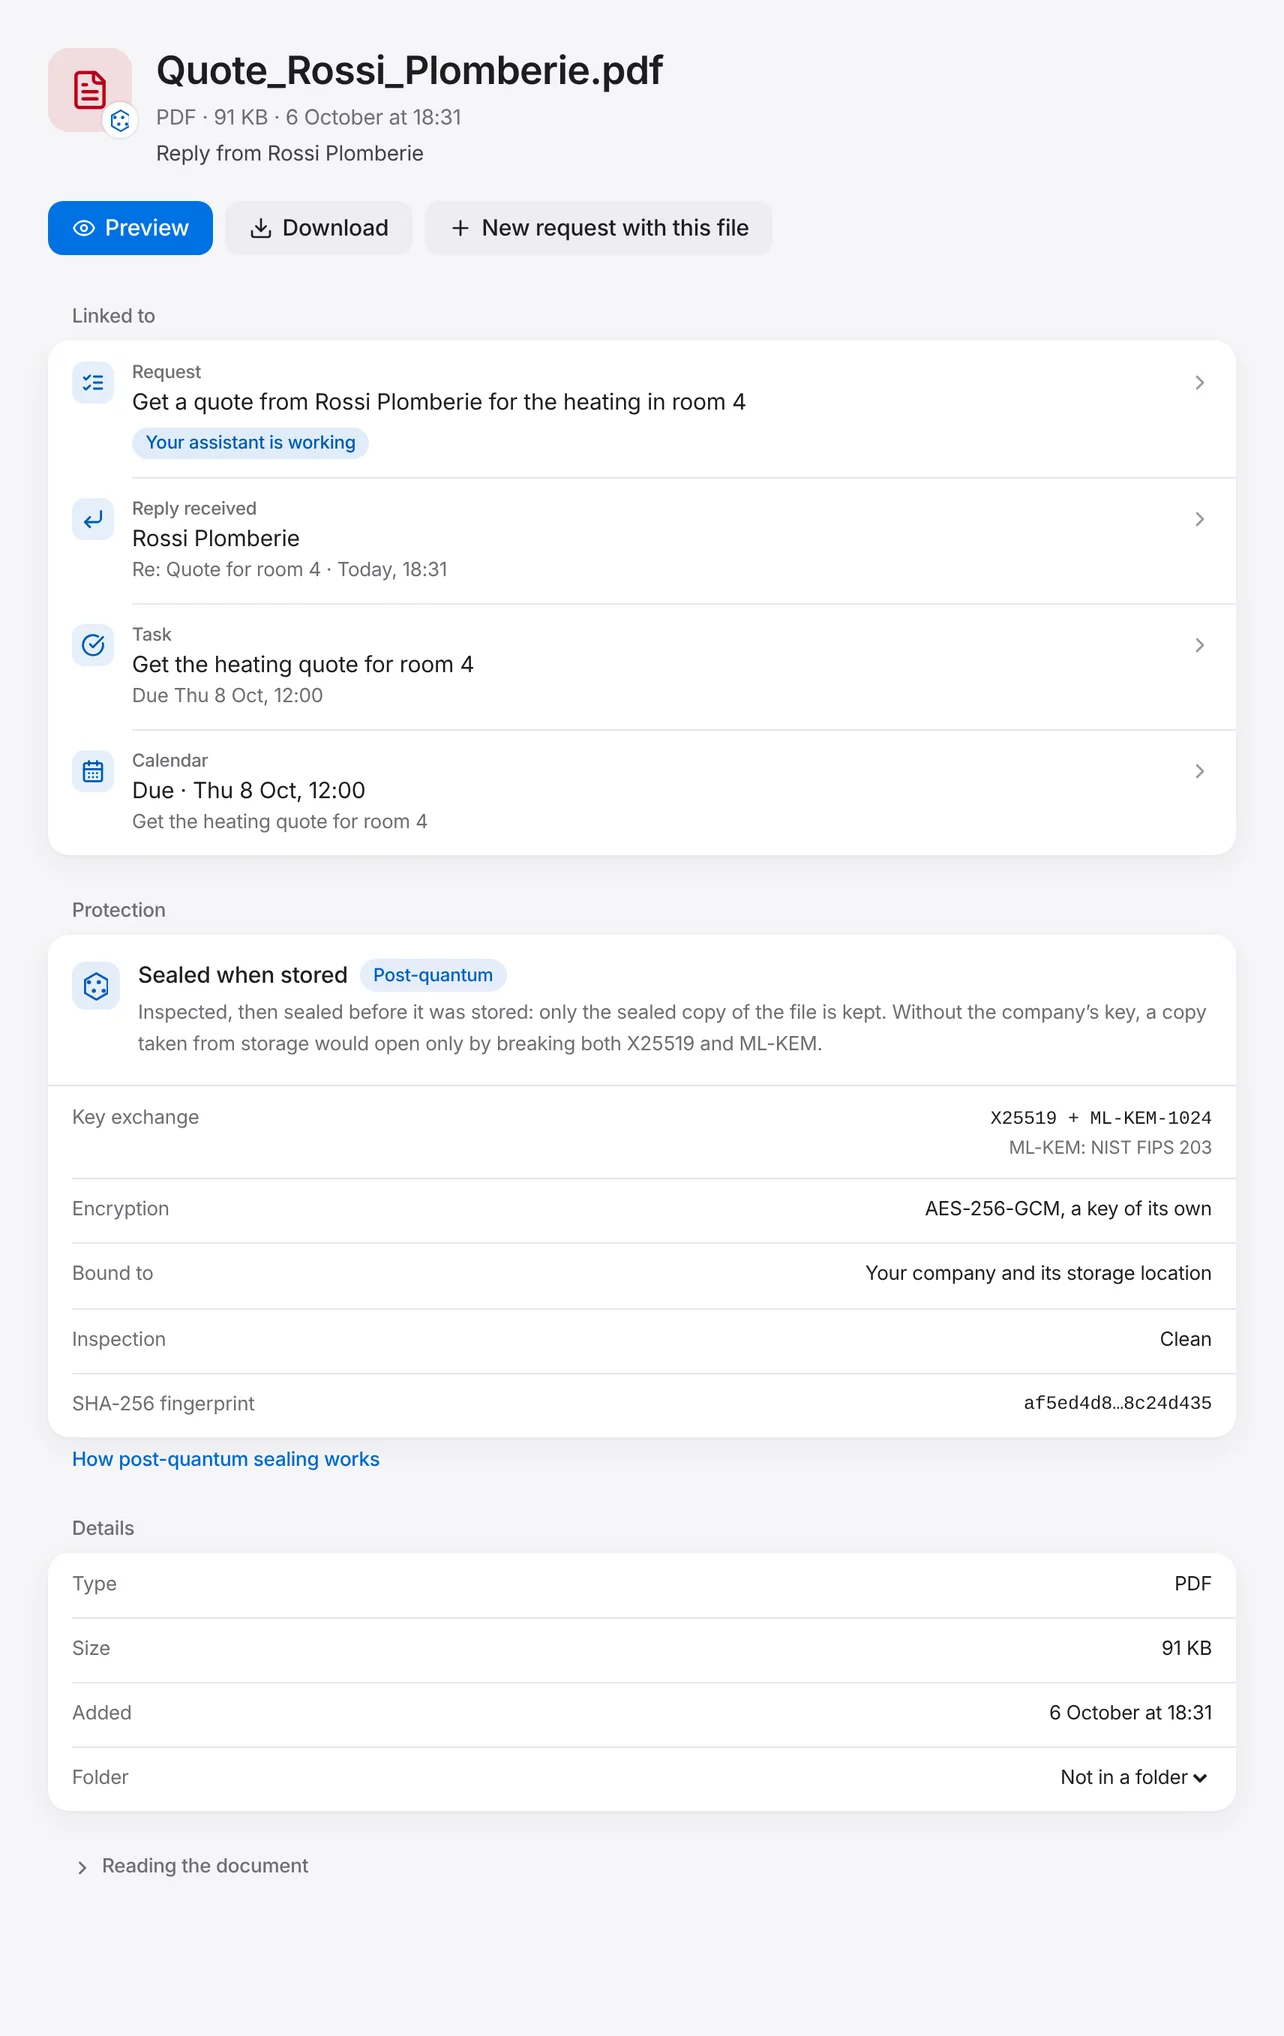
Four short chapters, a minute and a half in all: why it matters now, how each document is sealed, what a quantum computer breaks and what it does not, and what is covered. Shown on the Documents screens of the platform and the iPhone app. In each chapter, the next move is yours.

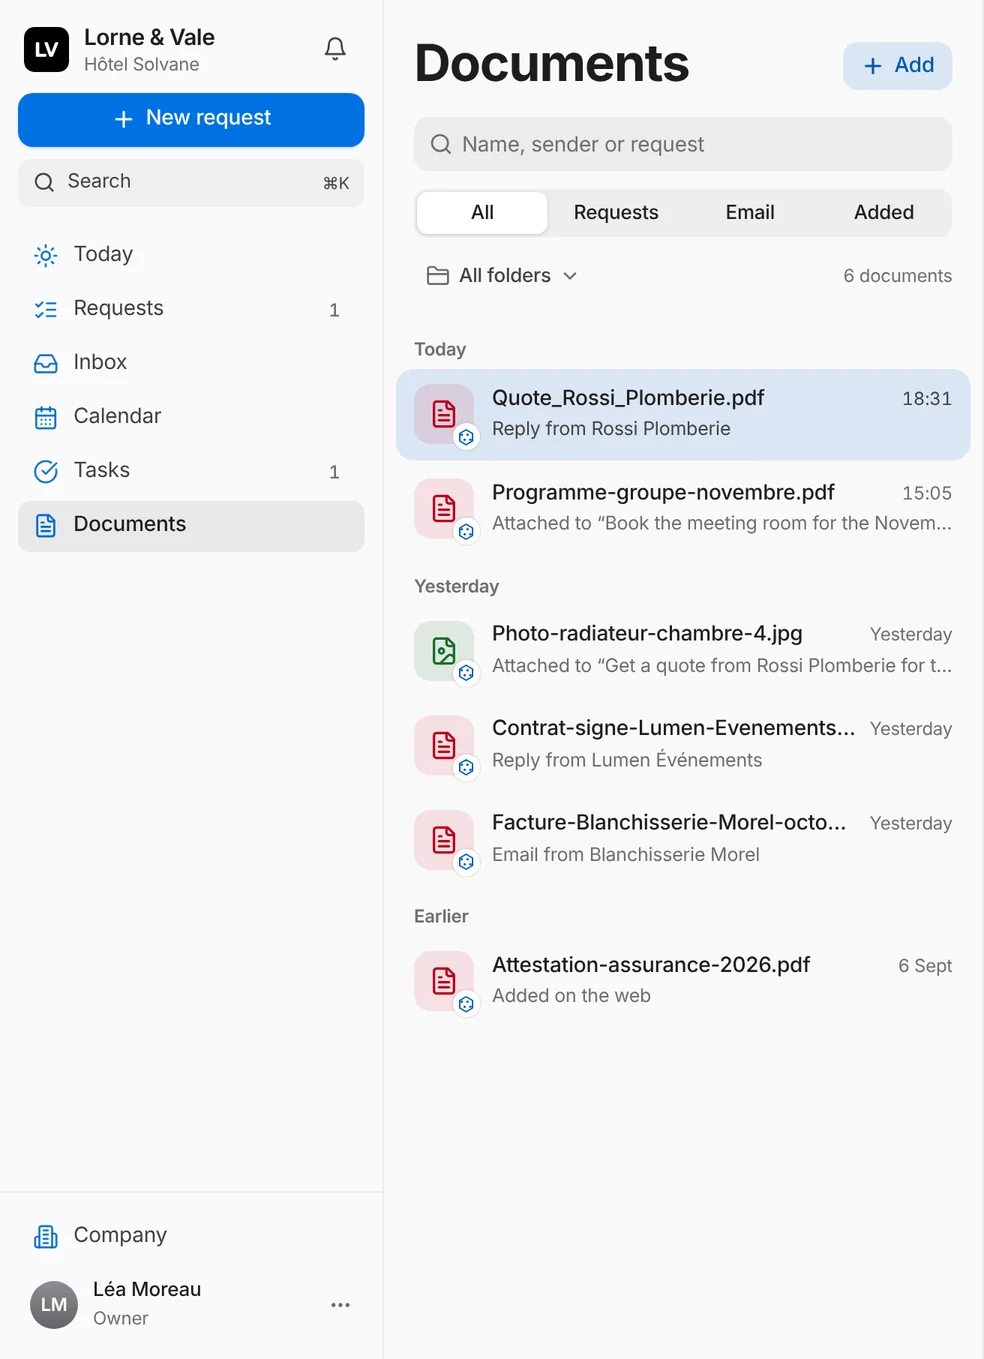
An interactive film in four short chapters, about ninety seconds, no sound. One: encrypted files can be copied today and opened later by a quantum computer, which is why protection has to start now. Two: a supplier’s quote arrives and is sealed when it is stored, inspected, with a key of its own locked by X25519 and ML-KEM-1024; its page on the web platform and in the iPhone app shows every fact. Three: Shor’s algorithm breaks RSA and elliptic curves, AES-256 and ML-KEM-1024 hold, and the two locks together mean one can fall while the other holds. Four: what the protection covers and what it does not.

Lorne & Vale: a supplier’s quote on the Documents screen of the web platform, sealed with X25519 and ML-KEM-1024

Sources: NIST FIPS 203, August 2024 · NIST IR 8547, initial public draft, November 2024 · NIST IR 8105, April 2016 · EU coordinated implementation roadmap, June 2025 · ANSSI on post-quantum cryptography (in French). Nobody can say when a large quantum computer will exist. The protection does not wait for it.

1024

ML-KEM-1024The highest of the three NIST security levels, for every document.

3

Signatures on each checkpointOf your record: two post-quantum, one classical.

1

Fresh key per documentEvery file is sealed with a key of its own.

0

Ads or trackersNo advertising or analytics cookies. No data sales.

Six layers

Protection at every step

From the moment you type a request to the record kept years later.

Post-quantum

Every document, sealed twice over

Each document gets its own key, locked by two independent algorithms: one built to resist quantum computers, one proven over decades. To open it, an attacker would have to break both.

Technical detail
Content
AES-256-GCM, a fresh key for every document
Key protection
Hybrid X25519 + ML-KEM-1024, combined through HKDF
Standard
ML-KEM, NIST FIPS 203
Keys
Specific to your company
Downloads
In the browser, sealed to a one-time key created in your tab and never sent to our servers
Post-quantum

Private on the way, too

Between your device and Lorne & Vale, connections use hybrid post-quantum key exchange on iPhones with iOS 26 and on up-to-date browsers.

Technical detail
Protocol
TLS 1.3
Key exchange
X25519MLKEM768, hybrid
Supported by
iOS 26 and macOS 26, Safari 26, Chrome 131, Firefox 132 and later
Older devices
Classical TLS with forward secrecy
Post-quantum

A record no one can rewrite

Every action is chained to the one before it as it is written, so any change would show. Each checkpoint of the record is signed three times: twice with post-quantum signatures, once with a classical one.

Technical detail
Chain
SHA-256 over each entry and the one before it
Writes
Append-only, in an order set by the server
Checkpoint signatures
ML-DSA-87 (FIPS 204), SLH-DSA (FIPS 205) and Ed25519
Verification
Public keys kept in a registry, so a signature can be checked without any signing secret
Privacy

Names stay out of the analysis

Before any text is sent out for analysis, the names, email addresses and other identifiers it detects are replaced with neutral tokens. The keys to put them back are sealed, per company and per record.

See what is sent
Technical detail
Before sending
Detected identifiers replaced with tokens
Token maps
Sealed, bound to your company and to the record
Analysis provider
OpenAI API, receiving de-identified text
Decisions
Commitments always need a person’s approval
Access

Only your team, only your data

Face ID on iPhone. Two-step verification on the web. And database rules that check every single row against your company.

Technical detail
iPhone
Face ID lock, encrypted offline cache
Web
Two-step verification with recovery codes, hardened sessions, CSRF protection and a strict content security policy
Database
Row-level security on every table
Roles
Owner, admin and manager
Access
Only people your company invites
European Union

Hosted in Europe

Your workspace data and files are stored in the European Union, and the application runs there too, close to your data.

Technical detail
Database and files
Supabase, European Union (eu-west-1)
Application
Vercel, European Union (dub1)
Transfers
EU-US Data Privacy Framework or the European Commission’s Standard Contractual Clauses

The record

Try to rewrite history

Each action is chained to the one before it with a SHA-256 fingerprint, and checkpoints of the chain are signed. Tap a line to alter it: every fingerprint after it changes, and the checkpoint’s signature no longer matches.

Action timelineLinen delivery

Checkpoint signed

ML-DSA-87, SLH-DSA and Ed25519

VerifiedNo longer matches

Tap a line to alter it.

Demonstration

What the analysis sees

Before an email is sent out for analysis, the names, email addresses and phone numbers found in it are replaced with neutral tokens, and the key to put them back stays in your workspace, sealed. Here is what the platform’s de-identification gives for a guest’s email.

Inbox, Hôtel SolvaneSent for analysis

FromCamille{{LV_PII_FIRST_NAME_1}} Durand{{LV_PII_LAST_NAME_1}} <camille.durand@example.com{{LV_PII_EMAIL_1}}>

Hello,

There is no heating in room 4. We arrived this evening with our two children. Could someone come tonight, or could we move to another room? You can reach me on 06 12 34 56 78{{LV_PII_PHONE_1}}.

Thank you,
Camille{{LV_PII_FIRST_NAME_1}} Durand{{LV_PII_LAST_NAME_1}}

The same email as it is sent for analysis: the first name, last name, email address and phone number are each replaced by a token.

In short

Comes back with tokens{{LV_PII_FIRST_NAME_1}} {{LV_PII_LAST_NAME_1}}, in room 4, reports no heating on arrival with two young children, and asks for a technician or another room tonight.

Put back in your workspaceCamille Durand, in room 4, reports no heating on arrival with two young children, and asks for a technician or another room tonight.

Suggested reply

Comes back with tokensHello {{LV_PII_FIRST_NAME_1}} {{LV_PII_LAST_NAME_1}}, we are very sorry about the heating in room 4. Our duty team is checking it now, and we will come back to you shortly.

Put back in your workspaceHello Camille Durand, we are very sorry about the heating in room 4. Our duty team is checking it now, and we will come back to you shortly.

4 identifiers replaced: first name, last name, email address, phone number.

Only the text with tokens leaves for analysis.

The requests you hand over are de-identified the same way before your assistant plans them.

Peace of mind

What if…?

The questions we are asked most, answered plainly.

What if someone copied our servers?

Your documents would be useless to them. Each one is sealed with its own key, and those keys are locked by a master key kept outside the database. The rest of your workspace is encrypted on disk by our host in Europe and walled off by access rules on every table.

Post-quantum encryption

What if a quantum computer arrived tomorrow?

Your documents are sealed with ML-KEM-1024, built to resist it, on top of X25519. Their content is encrypted with AES-256, and your record is signed with two independent families of post-quantum signatures.

NIST FIPS 203, 204 and 205

What if someone stole my password?

A password is not enough. Owners and administrators must turn on two-step verification, and every account that has it must give its code to sign in. On iPhone, the app opens with Face ID.

Two-step sign-in

What if I lost my iPhone?

The app is locked with Face ID, and what it keeps for offline use is encrypted. Your workspace stays closed to strangers: only the people your company invites can get in.

Face ID

What if someone rewrote the history?

It would show. Each action is chained to the one before it and each checkpoint of the chain is signed three times. A single change breaks everything after it.

Signed record

What if our clients’ names were sent for analysis?

Tokens go in their place. Before any text is sent out for analysis, detected names, email addresses and other identifiers are replaced with neutral tokens, and the keys to put them back are sealed.

De-identification

What if the assistant went too far?

It stays inside its limits. It writes only to the addresses in the request, sends at most six emails in seven days, is built to bring every commitment back to you, and you can pause it at any time. Only an owner, admin or manager can hand it email work.

Built-in limits

What if we stopped working together?

Your data stays yours. Download an export at any time, then close the company in its settings: its data is erased within minutes. Ask us by email and it is done within one week at the latest. The owner can also destroy your company’s key: your sealed documents can then no longer be opened.

Cryptographic erasure

Your rights

Your data
Your rules

For your company’s content, Lorne & Vale acts only on your instructions, under a data processing agreement. You can access, correct, export or delete your data. We reply to every request within 24 hours, and closing the company in its settings erases its data within minutes.

The Lorne & Vale app, locked and ready to unlock with Face ID

For your IT team

The technical summary

LayerWhat we useStandard
Documents at restAES-256-GCM per document, key wrapped with hybrid X25519 + ML-KEM-1024, company-specific keysNIST FIPS 203
In transitTLS 1.3 with hybrid X25519MLKEM768 on supporting devices, forward secrecy otherwiseIETF hybrid key exchange
Record integritySHA-256 hash chain, append-only; checkpoints signed with ML-DSA-87, SLH-DSA-SHA2-128s and Ed25519NIST FIPS 204 and 205, RFC 8032
Text analysisDetected identifiers replaced with tokens before sending; sealed token mapsGDPR data minimisation
IdentityFace ID on iPhone; two-step verification with recovery codes on the web; accounts created only by invitation from your companyRFC 6238
IsolationPostgreSQL row-level security on every tableLeast privilege
HostingDatabase, files and application in the European UnionGDPR

Questions from
your security team?

We walk your IT team through every layer before you start.